NIS2 mapping: what your auditor asks for.
Which rules ask for password screening, exactly what they ask, what PasswordRadar covers and what stays with your identity provider, and what to put in your compliance file.
- Updated
How the check maps to the rules you’re measured against
Facts and citations, not legal advice.
NIST SP 800-63B-4
Section 3.1.1.2: when a password is set or changed, the verifier SHALL compare it against a blocklist of commonly used, expected or compromised passwords, and the guidance names context-specific words such as the name of the service, the username and derivatives of them. NIST drops composition rules and periodic rotation; the Czech decrees below still require a change at least every 18 months.
PasswordRadar is that blocklist check, with your organisation’s and services’ names in early access; the username and its derivatives stay with your identity provider, because we never receive them.
Final version, 2025; supersedes Revision 3. NIST SP 800-63B-4 (PDF) (opens in a new tab)
NIS2
Directive (EU) 2022/2555, Article 21(2)(g), “basic cyber hygiene practices and cybersecurity training”, and (i), “human resources security, access control policies and asset management”. Screening every new password against a blocklist is a measure you can document under both.
- Czech Republic
- Act No. 264/2025 Sb. on Cybersecurity, in force since 1 November 2025, supervised by NÚKIB. Security-measure decrees No. 409/2025 Sb. (higher obligations) and No. 410/2025 Sb. (lower obligations).
- Slovakia
- Act No. 69/2018 Coll. on Cybersecurity as amended by Act No. 366/2024 Coll., in force since 1 January 2025, supervised by NBÚ.
Czech password rules
The decrees’ primary requirement is multi-factor authentication, or continuous authentication on a zero-trust model: Decree No. 409/2025 Sb., § 19(2), and Decree No. 410/2025 Sb., § 8(2); until then, cryptographic keys or certificates (§ 19(2)(b), § 8(3)). Decree No. 409/2025 Sb. also requires a register of the accounts that don’t meet it yet, with the reason (§ 19(3)). The password rules below apply while an account still signs in with a password alone.
Screening still matters once you have MFA: the password is still one of the factors, and NIST SP 800-63B-4 requires the blocklist check whenever a password is set or changed, whatever else protects the account.
| Rule | No. 409/2025 Sb. | No. 410/2025 Sb. | Who covers it |
|---|---|---|---|
| No “simple and commonly used passwords” | § 19(4)(f)(1) | § 8(4)(e)(1) | PasswordRadar |
| No passwords built from repeated characters, the login name, the email address or the system name, “or in a similar way” | § 19(4)(f)(2) | § 8(4)(e)(2) | Partly PasswordRadar. Masks, patterns and the brute-force space cover part of it; tailored generation (early access) adds context words such as your organisation’s and systems’ names. Each user’s own login name and email address stay with your identity provider: we never receive them. |
| At least 12 characters for users, 17 for administrators, 22 for technical accounts | § 19(4)(a) | § 8(4)(a) | Your identity provider |
| A change at least every 18 months | § 19(4)(e) | § 8(4)(d) | Your identity provider |
| No reuse of the last 12 passwords | § 19(4)(f)(3) | § 8(4)(e)(3) | Your identity provider |
| Accept passwords of at least 64 characters | § 19(4)(b) | Not required | Your identity provider |
Our English summary; the Czech text is binding: Decree No. 409/2025 Sb. (opens in a new tab), Decree No. 410/2025 Sb. (opens in a new tab). Context only: neither law nor decree names a product.
GDPR
No end-user data in API calls: no password, username or email address, only six characters of a salted hash. We receive your key and your server’s IP address. EU-hosted. Minimal logging: key ID, IP address, timestamp, response code and latency per request; web-server logs, which record the prefix with the calling IP address, are deleted within 15 days.
The operator, KnownPass s.r.o., is a Czech company under EU law.
For your compliance file
What an auditor or a supplier review asks for, in one place.
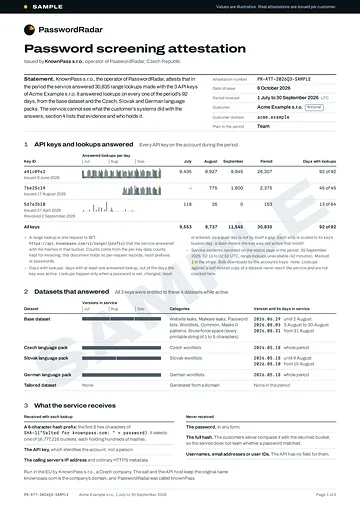 Sample attestation, PDF, 2 pages, about 120 KB
- Control
- Every new or changed password is checked against a blocklist of commonly used, expected or compromised passwords, as NIST SP 800-63B-4 asks, and against your organisation’s own names (early access).
- Mapping
- NIST SP 800-63B-4, section 3.1.1.2. Directive (EU) 2022/2555, Article 21(2)(g) and (i). Decree No. 409/2025 Sb., § 19(4)(f)(1), and Decree No. 410/2025 Sb., § 8(4)(e)(1); in part § 19(4)(f)(2) and § 8(4)(e)(2).
- Evidence
- With the Team plan, a per-customer, dated attestation for your auditors. The sample shows exactly what it covers.
- Operator
- KnownPass s.r.o., a Czech company under EU law and the GDPR, with no investors.
- Sub-processors
- Hetzner Online GmbH, Germany: the API and the dataset. WEDOS Internet, a.s., Czech Republic: this website. Proton AG, Switzerland: email. Hosting and processors
- Exit guarantee
- If PasswordRadar ever shuts down, you can download every dataset you are entitled to, free or paid, and keep self-hosting it forever.
Want to shape the product first? Apply as a design partner.